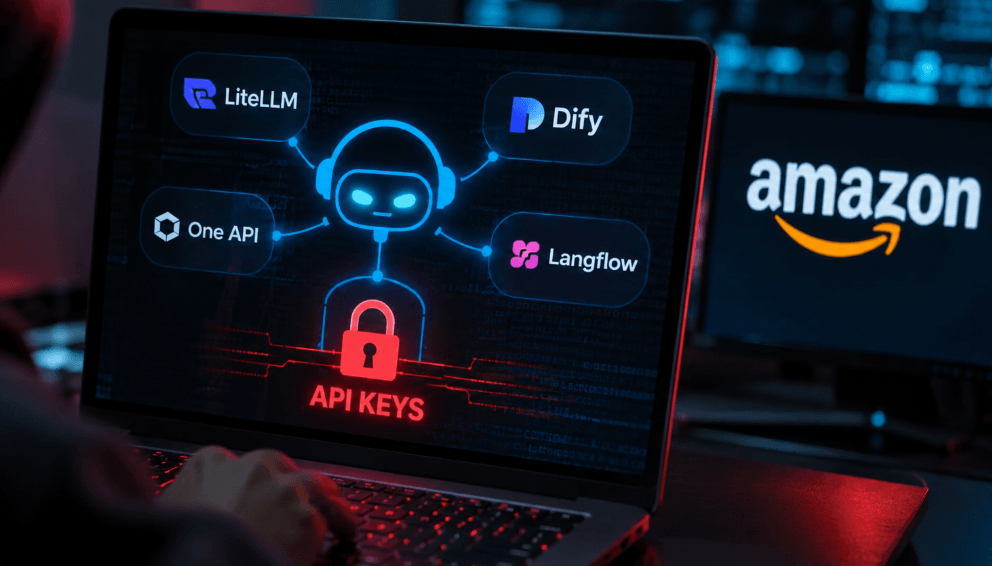
Amazon’s threat intelligence researchers have uncovered a cyberattack campaign in which attackers used autonomous artificial intelligence agents to identify vulnerabilities in publicly accessible AI applications and steal valuable API credentials. The operation targeted platforms including LiteLLM, Dify, One API and other services that manage access to large language models.
The findings highlight a growing cybersecurity threat: attackers using AI-powered automation to obtain credentials that can finance and support further malicious activity.
Amazon Identifies AI Agents Stealing API Keys
According to Amazon’s threat intelligence team, attackers deployed AI agents to scan internet-facing applications for weaknesses that could expose API keys belonging to major AI service providers.
Researchers discovered the activity through Amazon’s MadPot network, which uses decoy servers to observe suspicious behavior.
Between October 3 and mid-November 2026, the agents interacted with these servers and inadvertently revealed operational records, including instructions, attack strategies and reported findings.
Amazon said it could not independently verify every outcome described in the captured records.
However, researchers assessed with moderate confidence that the attackers used ARTEX, an open-source AI penetration-testing framework.
How the Automated Attacks Operated
ARTEX allows an operator to assign a target and objective to an AI-powered system. A planning agent divides the objective into smaller tasks, while worker agents execute security tools and analyze results using large language models.
In the campaign identified by Amazon, agents reportedly followed a recurring process: locating exposed AI applications, extracting stored credentials, testing whether those credentials remained valid and collecting working keys for future use.
The attackers prioritized AI gateways capable of storing credentials for multiple providers, potentially allowing one compromised application to expose numerous accounts.
LiteLLM, Dify and Other AI Applications Targeted
The captured records identified several targeted applications, including:
-
AI gateways: LiteLLM, One API, New API, Veloera and Sub2API.
-
AI development platforms: Dify, FastGPT, Langflow and RAGFlow.
-
AI interfaces and tools: Open WebUI, LobeChat and Ollama.
Attack methods included default administrator credentials, incomplete installations, exposed configuration files, authentication weaknesses and known software vulnerabilities.
Researchers also identified attempts to exploit server-side request forgery vulnerabilities to access cloud metadata services.
The agents searched GitHub repositories, software packages, container images, notebooks and public internet resources for exposed credentials.
Known Security Vulnerabilities Raise Concerns
Amazon’s findings referenced several security weaknesses affecting AI platforms.
Langflow vulnerability CVE-2025-3248 allows remote code execution without authentication in versions before 1.3.0. The vulnerability was added to the Cybersecurity and Infrastructure Security Agency’s Known Exploited Vulnerabilities catalog in May 2025.
RAGFlow vulnerability CVE-2026-28797 involves server-side template injection that can enable authenticated users to execute operating system commands.
Researchers also documented an authentication bypass involving the isCliRequest header in One API-related systems.
Cloudflare Reports ARTEX-Related Security Incidents
Cloudflare separately reported investigating incidents involving ARTEX and related AI security-testing frameworks.
In one case, attackers obtained an account-level API token associated with a compromised continuous integration and deployment environment.
The token lacked IP restrictions and rate limits, allowing extensive unauthorized activity.
Investigators observed approximately 400 database dump requests within one hour, although Cloudflare did not confirm whether those requests successfully retrieved information.
Attackers also created Cloudflare Worker scripts with names beginning with artex-, artex-pgrecon-, artex-pgw- and artex-do-.
The activity exceeded 69 requests per minute and included attempts to maintain access and validate third-party application sessions.
Microsoft and FBI Warn About Growing Threats
Microsoft has also documented attackers using agentic AI tools to search GitHub repositories for exposed credentials, including AI inference API keys.
Meanwhile, the FBI issued a November 2026 FLASH alert warning that attackers had used ARTEX against organizations across multiple industries since at least August.
Earlier reported incidents included attacks targeting South Korean financial institutions that exposed personal information associated with approximately 67,000 individuals.
Amazon’s researchers also identified a separate campaign in which AI agents attempted to bypass identity verification at cryptocurrency exchanges using deepfake technology.
How Organizations Can Protect AI Infrastructure
Amazon emphasized that the underlying vulnerabilities were largely familiar security problems, rather than entirely new attack techniques.
The significant difference is the speed and persistence that autonomous AI agents bring to exploitation attempts.
Security teams should prioritize several protective measures:
-
Replace default administrator credentials and secure unfinished installations.
-
Update vulnerable AI applications and management interfaces.
-
Regularly scan repositories, configuration files and container images for exposed secrets.
-
Rotate compromised API keys immediately.
-
Restrict API tokens by expiration date, permissions and authorized IP addresses.
-
Monitor unusual AI service usage, unexpected spending and suspicious account activity.
-
Review security logs for known ARTEX indicators and unauthorized Cloudflare Worker deployments.
AI-Powered Cyberattacks Increase Pressure on Security Teams
Amazon’s investigation demonstrates how autonomous AI agents can accelerate existing cyberattack techniques, particularly against organizations operating AI gateways and model-management platforms.
Although the researchers could not verify every reported compromise, the findings underscore the importance of securing AI infrastructure with the same controls applied to other critical production systems.
As AI adoption expands across American businesses, protecting API credentials, limiting privileged access and maintaining updated software will remain essential to reducing exposure to automated cyberattacks.
William Faulkner is a contributor to Columbuspost.com, covering a broad range of topics including news, politics, business, technology, sports, entertainment, and lifestyle. He focuses on delivering clear, accurate reporting and useful information that helps readers stay informed about current events and developments. His work highlights stories that matter to local and wider communities, with an emphasis on relevance, clarity, and providing readers with a balanced understanding of the issues shaping everyday life.


More Stories
Google Brings Personalized Gemini AI to Android Auto With Gmail, Maps and Calendar Integration
WhatsApp Is Redesigning Its Android App With a New Navigation Bar
iPhone 18 Pro Max Still Uses Qualcomm Modem in U.S., Teardown Confirms